
Guides
Task-based walkthroughs with complete config files. Each pair is a server, run on a machine outside the censored network, and a client, run on the user's device, which exposes a local SOCKS5 or mixed port for apps.
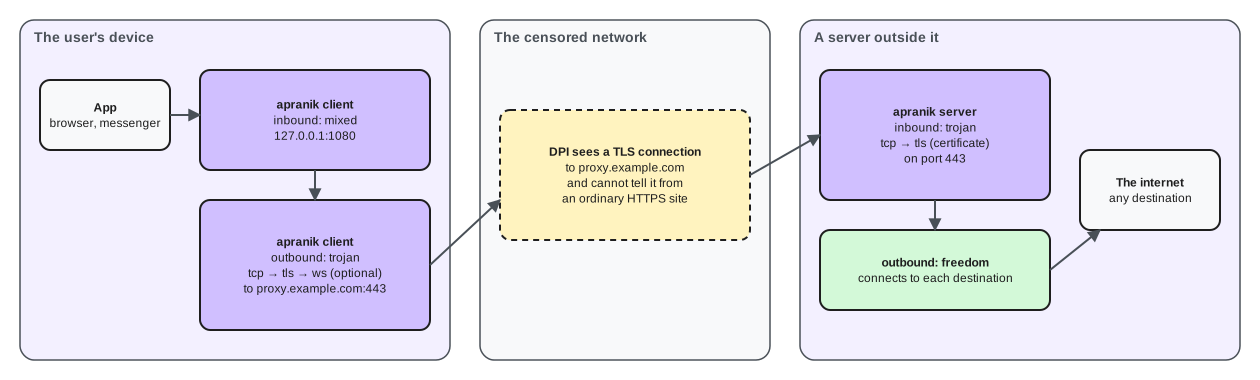
What these guides assume
Replace proxy.example.com, the passwords and the certificate paths with your own. Check a file before running it:
sh
apranik check -config server.json
apranik run -config server.json
A client's local port with no users is open to every app on the machine.
The protocol and transport pages describe every setting: trojan, tls, ws, httpupgrade.
The guides
- Run Trojan over TLS: A server that looks like an HTTPS site, and a client that reaches it.
- Run Trojan over WebSocket behind a CDN: A server behind a CDN that relays WebSocket, and a client that reaches it.
- Run a local proxy with no server: A proxy on your own machine that needs no server.
- Hide the server name: Keep the server's name out of the TLS handshake.